How Do Founders Pass VC Code Reviews

How Do Founders Pass VC Code Reviews? Ultimate Guide

VC Due Diligence Prep: 7 Architecture and Codebase Red Flags That Freeze Series A/B Funding (And How to Fix Them)

VC due diligence can make or break a funding round. Founders often spend months perfecting their pitch deck. However, many overlook the technical review that follows. This is where deals frequently stall or collapse entirely.

Picture a founder who has just wrapped up a strong pitch meeting. The investor seems interested and asks to move forward with due diligence. Weeks later, the deal quietly stalls. Often, the real reason is not the business model or the market opportunity. Instead, it is something buried in the codebase that nobody flagged early enough.

Investors want confidence that your product can scale. They want proof that your team can move fast without breaking things. If your architecture or codebase raises concerns, VC due diligence can freeze your Series A or Series B round. This guide walks through seven common red flags. It also explains how founders can fix them before investors ever ask.

Each red flag below reflects a pattern seen repeatedly across failed and delayed funding rounds. None of them are unusual or unique to a single industry. Instead, they represent common growing pains that many startups face as they scale from a small team to a larger, more complex organization.

Why VC Due Diligence Goes Deeper Than the Pitch

Many founders assume due diligence mainly covers financials and market size. In reality, technical due diligence has become just as important. Investors increasingly bring in engineering experts to review your codebase. They examine scalability, security, and long-term maintainability. Some funds now employ dedicated technical partners solely for this purpose, reflecting how much weight engineering quality carries in modern funding decisions.

This shift makes sense. A great product idea means little if the underlying system cannot support growth. Consequently, founders who prepare early gain a real advantage. Understanding common red flags helps you address issues before they threaten your funding timeline.

Technical due diligence typically involves a mix of interviews, automated code analysis, and hands-on review by experienced engineers. Investors want to understand not just what your product does today, but whether it can support the growth projections in your pitch deck. A mismatch between your technical reality and your growth story can quickly raise doubts, even if every other part of your business looks strong.

Red Flag 1: Poor Code Documentation of VC

Investors expect to see clear documentation. Without it, technical reviewers struggle to understand how your system works. This slows down the entire due diligence process and raises immediate concerns.

The fix: Document your architecture, key workflows, and API structures. Keep documentation updated as your product evolves. Clear documentation signals a mature, well-managed engineering team. Consider assigning ownership of documentation to specific team members, so it does not fall through the cracks as your roadmap shifts.

Red Flag 2: High Technical Debt

Technical debt accumulates when teams prioritize speed over code quality. While some debt is normal, excessive debt raises red flags. It suggests future scalability problems and higher maintenance costs.

The fix: Conduct regular code reviews and refactoring sprints. Track technical debt using a simple internal system. Show investors that you actively manage and reduce debt over time. Many founders find it helpful to dedicate a fixed percentage of each sprint specifically to debt reduction, rather than treating it as an afterthought.

Red Flag 3: Lack of Automated Testing

Manual testing alone cannot keep up with a growing codebase. Investors often ask about test coverage during VC due diligence. Low or missing automated tests suggest higher risk of bugs and downtime.

The fix: Implement unit, integration, and end-to-end tests. Aim for solid coverage across critical features. Automated testing also speeds up future development, which investors appreciate. It also reduces the chance of production incidents during a high-visibility growth period, when your reputation with customers and investors matters most.

Red Flag 4: Weak Security Practices

Security gaps are a serious concern for any investor. This includes poor access controls, unencrypted data, or outdated dependencies. A single vulnerability can damage trust and delay funding significantly.

The fix: Perform regular security audits. Update dependencies consistently. Implement strong authentication and data encryption practices. Document your security protocols clearly for investor review. If your product handles sensitive customer data, consider pursuing relevant compliance certifications early, since investors in regulated industries often ask about them directly.

Red Flag 5: Single Points of Failure

If your system relies heavily on one server, one engineer, or one vendor, this creates risk. Investors want to see resilience built into your architecture. Single points of failure suggest fragile infrastructure.

The fix: Build redundancy into critical systems. Avoid over-reliance on any single team member for core knowledge. Cross-train your engineering team and document key processes thoroughly. Investors often ask what would happen if a key engineer left tomorrow, so having a clear answer builds confidence.

Red Flag 6: Scalability Concerns

Some codebases work fine at small scale but struggle under growth. Investors want evidence that your architecture can handle rapid user growth. Poor database design or inefficient code often signals future scaling problems.

The fix: Stress test your systems before scaling rapidly. Optimize database queries and consider scalable infrastructure solutions early. Show a clear plan for handling increased demand. Presenting load testing results during due diligence can turn this red flag into a genuine strength.

Red Flag 7: Messy or Inconsistent Codebase Structure

A disorganized codebase slows down new developers and increases error rates. Investors view this as a sign of weak engineering discipline. It can also indicate rushed development without proper planning.

The fix: Establish clear coding standards across your team. Use consistent naming conventions and folder structures. Regularly review code quality to maintain consistency as your team grows. Automated linting tools can help enforce these standards without adding extra manual review burden on your senior engineers.

How to Prepare for VC Due Diligence Successfully

Preparation is the key to passing technical due diligence smoothly. Start by conducting an internal audit before investors request one. Identify weak areas and address them proactively. This builds investor confidence and speeds up the funding process.

Additionally, involve your engineering leadership early in fundraising conversations. They can help answer technical questions with clarity and confidence. This reduces friction and demonstrates strong internal alignment. Investors notice when a founder and their technical lead speak with one voice, and it builds trust quickly.

Prepare your engineering team for the tone of these conversations as well. Technical due diligence can feel like an audit, which sometimes puts engineers on the defensive. Set expectations ahead of time that this is a normal part of fundraising, not a personal critique. A calm, collaborative team usually leaves a stronger impression on investors than one that seems rattled by tough questions.

Finally, consider working with outside experts who specialize in due diligence preparation. An objective review often catches issues your internal team might miss. This extra layer of preparation can make a meaningful difference during high-stakes funding rounds.

It also helps to create a simple technical summary document for investors. This should outline your architecture, security practices, testing approach, and scalability plans in plain language. Having this ready in advance saves time during the fundraising process and shows investors that your team is organized and confident. Many founders underestimate how much a well-prepared technical narrative can speed up closing a round.
How Do Founders Pass VC Code Reviews

Conclusion

VC due diligence can feel intimidating, especially for first-time founders. However, understanding common architecture and codebase red flags puts you in control. By addressing these issues early, you protect your funding timeline and build stronger investor trust.

Do not wait until investors raise concerns. Get ahead of the process now. A little preparation now can save weeks of back-and-forth later, and it signals to investors that your team takes engineering discipline seriously. Download the VC Due Diligence Checklist with Ouriken Consulting, and walk into your next funding round fully prepared.

Frequently Asked Questions

1. What is VC due diligence in simple terms?

It is the process investors use to evaluate your business, including financials, market position, and technical infrastructure, before finalizing funding.

2. Why does technical due diligence matter for startups?

Investors want confidence that your product can scale reliably. Technical due diligence helps them assess risk before committing capital.

3. How early should founders prepare for VC due diligence?

Ideally, founders should prepare months before fundraising begins. Early preparation reduces surprises and builds stronger investor confidence.

4. Can technical red flags actually stop a funding round?

Yes, significant red flags can delay or completely freeze funding, especially if investors view them as high risk.

5. Should startups hire outside help for due diligence prep?

Many founders benefit from outside expertise. An objective review often uncovers issues that internal teams may overlook.
Also Read:

How Financial Regulations in India Shape Fintech Growth?

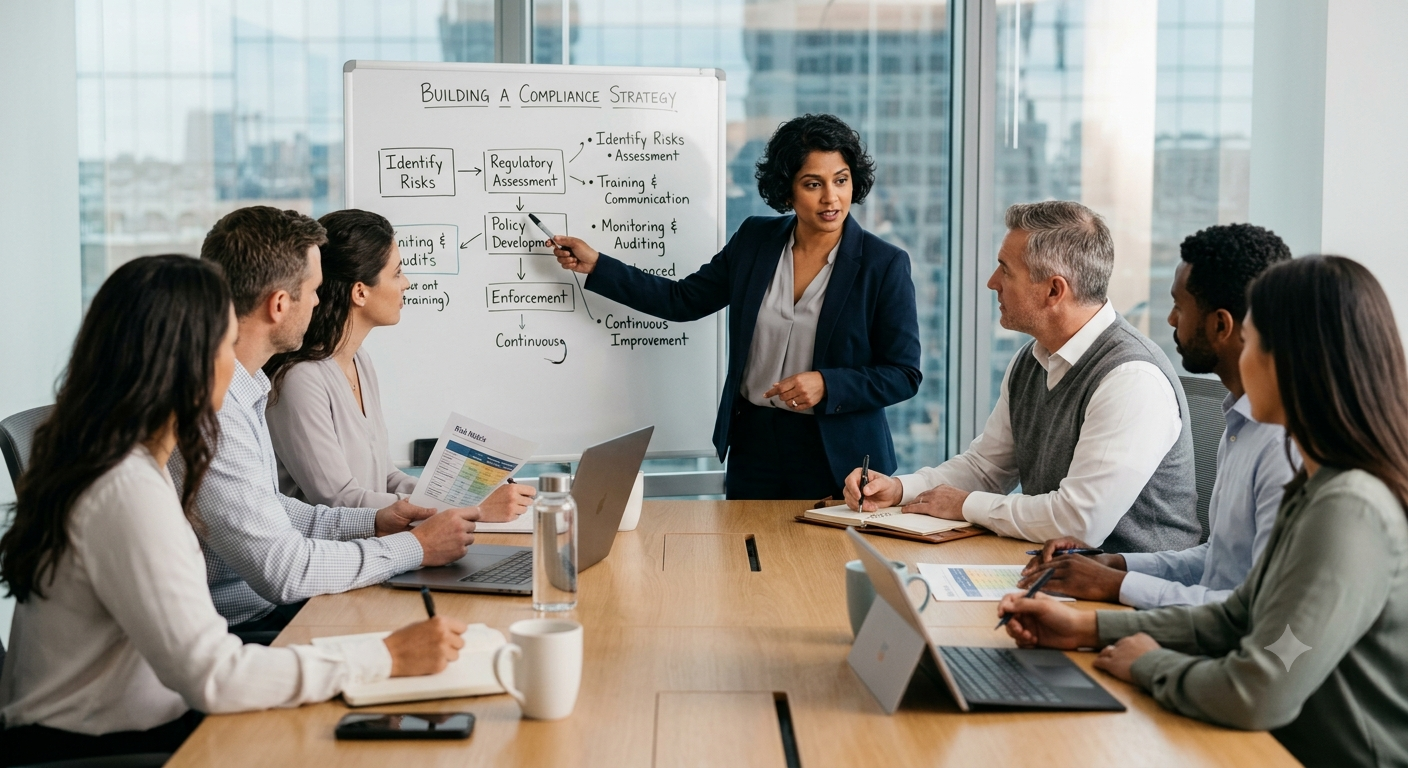
How Do You Build a Compliance Strategy? Ultimate Guide

How Do You Build a Compliance Strategy?

How Do You Build a Compliance Strategy? Ultimate Guide

Compliance Automation: Using AI to Stay Ahead of Regulations

Regulations change constantly. New rules appear across finance, data privacy, and payments every year. Keeping up manually drains time and increases risk. This is where compliance automation becomes valuable. AI now helps businesses track, interpret, and apply regulatory changes faster than ever before.

This guide explains how AI-powered compliance automation works. It also shows practical steps for adopting it, even without a large legal or compliance team. Whether you run a fintech startup or a growing enterprise, these strategies apply directly to your business.

Why Traditional Compliance Methods Fall Short

Traditional compliance relies heavily on manual review. Teams read updates, interpret language, and adjust policies by hand. This process is slow. It is also prone to human error.

Furthermore, regulatory bodies release updates frequently and without much warning. A single missed update can lead to costly penalties. Small teams often struggle to monitor every relevant regulation across multiple regions.

As businesses expand into new markets, compliance complexity multiplies. Different countries enforce different rules. Consequently, manual tracking becomes nearly impossible at scale. This is exactly where compliance automation proves its value.

The Real Cost of Non-Compliance

Non-compliance costs more than fines. It damages trust, delays product launches, and increases legal exposure. Additionally, repeated violations can trigger stricter regulatory scrutiny going forward.

Many businesses underestimate these hidden costs. They focus only on avoiding direct penalties. However, reputational damage often outlasts any single fine. Proactive compliance protects both finances and brand reputation.

Customers and partners also notice compliance failures. A public violation can slow down partnership deals or investor conversations for months. Building a reliable compliance record, therefore, supports growth well beyond the regulatory department.

How AI Powers Compliance Automation

AI-driven compliance tools scan regulatory updates continuously. They flag changes relevant to your industry. Moreover, they can map new rules directly against your existing policies.

This process, once handled by large legal teams, now runs in the background. Machine learning models learn to recognize patterns across regulatory language. As a result, they can highlight risks faster than manual review ever could.

Real-Time Regulatory Monitoring

Real-time monitoring tools track changes from government agencies, financial regulators, and industry bodies. When something shifts, the system alerts your compliance team immediately.

This speed matters. Early awareness allows businesses to adjust policies before violations occur. In contrast, delayed awareness often leads to reactive scrambling and last-minute fixes.

Many platforms also let teams customize alert priority. High-risk regulatory changes trigger immediate notifications, while minor updates get grouped into weekly summaries. This filtering keeps teams focused on what truly matters.

Automated Policy Mapping

Beyond monitoring, AI tools can map regulations to internal policies automatically. They identify gaps between current practices and new requirements. Consequently, compliance teams spend less time searching and more time acting.

This mapping process also creates useful documentation. Auditors appreciate clear records showing how policies evolved alongside regulatory changes.

Why Manual Tracking No Longer Scales

Manual tracking worked when regulations changed slowly. That era has ended. Regulators now update rules more frequently, and enforcement has grown stricter across most industries.

A single compliance officer cannot realistically read every bulletin, guidance note, and amendment. Furthermore, cross-border businesses face multiplied complexity, since each region publishes its own updates on its own schedule. Automation closes this gap by working continuously in the background.

Building a Compliance Automation Strategy

Adopting compliance automation does not require a complete system overhaul. A phased approach works best for most businesses.

Step 1: Audit Your Current Compliance Process

Start by reviewing how compliance currently works. Identify manual bottlenecks. Note where delays or errors happen most often. This audit reveals where automation adds the most value.

Step 2: Choose the Right AI Compliance Tools

Not every tool fits every business. Look for platforms built for your specific industry, whether that is payments, healthcare, or general data privacy. Additionally, check integration options with your existing systems.

Trial periods help here. Test how well a tool handles real regulatory scenarios before committing long term. This hands-on testing prevents costly mismatches later.

Step 3: Train Staff on New Workflows

Automation works best alongside informed staff. Teams still need to understand alerts and act on them appropriately. Therefore, short training sessions should accompany any new tool rollout.

Encourage compliance staff to treat AI as a support system, not a replacement. Human judgment remains essential for complex regulatory decisions.

Step 4: Monitor and Refine Continuously

No automation system works perfectly from day one. Review alerts regularly. Adjust filters to reduce noise and improve accuracy. Over time, the system becomes more precise and more useful.

Building Better Audit Trails

Automated systems naturally create detailed logs of every action taken. This includes which regulation triggered an alert and how the team responded. Auditors value this level of detail highly.

Additionally, clear audit trails reduce the time needed for external reviews. Instead of reconstructing history manually, compliance teams simply export existing records. This efficiency saves both time and legal expense during audits.

Compliance Automation in the Payments Industry

Payment companies face some of the strictest regulatory environments. Rules around fraud prevention, data security, and cross-border transactions shift often. AI-powered compliance tools help payment businesses stay ahead of these changes.

For example, automated systems can flag suspicious transaction patterns instantly. They can also update fraud detection rules as new regulations emerge. Similarly, they help maintain accurate audit trails required by financial regulators.

This proactive approach reduces both regulatory risk and operational strain. Teams no longer chase every update manually. Instead, they focus on strategic decisions while automation handles routine monitoring.

Reducing Risk Without Increasing Headcount

Many payment businesses cannot afford large compliance teams. AI-powered automation closes this gap effectively. It allows small teams to manage complex regulatory environments confidently.

Finally, this efficiency creates room for growth. Businesses can expand into new markets without proportionally expanding their compliance staff.

Common Challenges in Compliance Automation

Adoption is not always smooth. Some businesses face resistance from staff accustomed to manual processes. Others struggle with poor data quality, which limits automation accuracy.

However, these challenges are manageable. Clear communication about benefits reduces resistance. Meanwhile, cleaning up data before automation improves results significantly. Addressing these issues early prevents frustration later.

Overcoming Integration Hurdles

Some businesses worry that new tools will not connect with existing systems. This concern is valid but often overstated. Most modern compliance platforms offer integrations with common accounting, CRM, and payment systems.

Before purchasing, confirm integration compatibility during the trial period. Ask vendors for case studies from similar businesses. This due diligence prevents costly surprises after implementation begins.

Keeping Humans in the Loop

Automation should support decision-making, not replace it entirely. Complex or unusual cases still need human judgment. Therefore, design workflows where AI flags issues and humans make final calls on ambiguous situations.

This balance protects your business from both over-reliance on automation and unnecessary manual workload. It also builds trust in the system among staff and leadership alike.

How Do You Build a Compliance Strategy?

Conclusion

Compliance automation transforms how businesses manage regulatory risk. AI-powered tools monitor changes, map policies, and reduce manual workload significantly. Small and mid-sized businesses, especially in payments and finance, benefit enormously from this shift.

Start with a clear audit. Choose tools suited to your industry. Train your team and refine your process over time. This structured approach keeps your business ahead of regulations rather than reacting to them.

Businesses that adopt compliance automation early gain a lasting advantage. They spend less time firefighting and more time growing. That shift alone justifies the investment for most organizations.

Ready to strengthen your compliance strategy even further? Build your authority with Digital Payment Guru and lead your industry with confidence.

Frequently Asked Questions

1. What is compliance automation? Compliance automation uses AI and software tools to monitor regulations, flag risks, and update policies with less manual effort.

2. How does AI help with regulatory compliance? AI scans regulatory updates continuously, maps them against internal policies, and highlights gaps that need attention.

3. Is compliance automation only for large companies? No. Many affordable tools exist for small and mid-sized businesses, especially in the payments and fintech space.

4. Can AI completely replace compliance teams? No. AI supports compliance teams by handling monitoring and documentation. Human judgment remains essential for complex decisions.

5. How quickly can a business implement compliance automation? Many businesses see initial results within a few weeks. Full integration typically takes a few months, depending on complexity.

Also Read:

How Do You Balance Data Mobility & Safety? Ultimate Guide

How Financial Regulations in India Shape Fintech Growth?

How India’s Financial Regulations Are Shaping Fintech Innovation

How Financial Regulations in India Shape Fintech Growth?

How India’s Financial Regulations Are Shaping Fintech Innovation

Introduction

India’s fintech sector is growing at a remarkable pace. Millions of people now use digital payments, lending apps, and online banking every day. Behind this growth sits a strong framework of financial regulations in India. These rules shape how fintech companies build products and reach customers.

This article explores how India’s financial regulations are shaping fintech innovation. You will learn which rules matter most, how they affect startups, and what founders should expect next. Business owners, technical managers, and digital marketers will find practical insight here. Additionally, this guide explains complex rules in simple terms.

India now has one of the largest digital payment markets in the world. This scale did not happen without careful oversight. Regulators and innovators have worked together, sometimes with friction, to build a system that millions trust every day.

The Regulatory Foundation Behind India’s Fintech Boom

India’s fintech growth did not happen by accident. The Reserve Bank of India, or RBI, built a strong foundation for digital finance. This foundation includes the Unified Payments Interface, known as UPI, which now processes billions of transactions each month.

The RBI also created clear licensing rules for payment banks and non-banking financial companies. These rules give fintech startups a path to operate legally. As a result, entrepreneurs know what steps to follow before launching a product. This clarity reduces risk for investors too.

Data protection has become a growing focus for regulators. The Digital Personal Data Protection Act sets rules for how companies collect and store user data. Fintech companies must follow these rules carefully. Consequently, product teams now build privacy into their apps from day one, not as an afterthought.

Regulatory sandboxes have also played a key role. The RBI allows selected startups to test new products in a controlled environment. This helps regulators understand new technology before writing formal rules. Meanwhile, startups get real feedback without facing the full weight of compliance too early.

The Securities and Exchange Board of India, or SEBI, also shapes fintech through rules for investment platforms and wealth-tech apps. Together, these bodies form a layered system of oversight. Each layer targets a different part of the financial ecosystem, from payments to lending to investing.

The Insurance Regulatory and Development Authority of India, known as IRDAI, plays a similar role for insurtech startups. This layered approach means fintech founders must understand more than one regulator, depending on which financial services they offer.

How Compliance Rules Push Financial Regulation Forward

Many founders assume regulation slows down innovation. In India’s fintech space, the opposite has often proven true. Clear rules create trust, and trust drives adoption among cautious users.

Know Your Customer, or KYC, requirements are a good example. These rules force fintech apps to verify user identity before opening an account. This process once took days using paper documents. Today, video KYC and Hadar-based verification make on-boarding fast and secure. Therefore, compliance rules pushed companies to build better technology.

Similarly, RBI guidelines on data localization require companies to store Indian payment data within the country. This rule pushed fintech firms to invest in local cloud infrastructure. In turn, this investment supported the growth of India’s broader technology ecosystem.

Payment aggregator and payment gateway rules also raised the bar for security. Companies must now meet strict standards before processing transactions. This has reduced fraud and increased consumer confidence in digital payments. In contrast, markets with weaker rules often see slower adoption due to trust issues.

Lending regulations have reshaped how digital lenders operate too. The RBI’s digital lending guidelines require clear disclosure of interest rates and fees. This protects consumers from hidden charges. Fintech lenders that comply well often see stronger customer loyalty as a direct result.

Similarly, rules around recovery practices have pushed lenders to build more respectful collection processes. Aggressive tactics that once damaged brand reputation are now restricted by law. This shift has encouraged fintech lenders to invest in better customer support systems instead.

Challenges Fintech Startups Face Under Current Financial Regulations

Regulation is not without its challenges for fintech startups. Compliance costs can be high, especially for early-stage companies. Building systems for KYC, data protection, and reporting requires time and money that small teams may not have.

Frequent regulatory updates also create uncertainty. The RBI and other bodies update guidelines regularly to keep pace with new technology. Startups must stay alert and adjust their products quickly. Otherwise, they risk falling out of compliance without realizing it.

Cross-border payment rules add another layer of complexity. Fintech companies working with international partners must navigate both Indian rules and foreign regulations. This dual compliance burden can slow product launches significantly.

Despite these challenges, most founders agree that strong regulation ultimately builds a healthier market. It filters out weak players and rewards companies that invest in proper systems. Thus, long-term winners in India’s fintech space tend to be those who treat compliance as a strategic advantage, not a burden.

Smaller startups often partner with compliance experts to manage this load. This allows founders to focus on product and growth while specialists handle regulatory details. This approach has become common across the industry.

Talent shortages also add pressure. Skilled compliance officers who understand both finance and technology are hard to find. Fintech companies often compete with banks and larger financial institutions for the same limited pool of experts. This drives up hiring costs for early-stage teams.

Investor expectations have shifted as a result of these challenges. Venture capital firms now look closely at a startup’s compliance readiness before writing a check. A strong regulatory foundation has become just as important as a strong product in fundraising conversations.

What’s Next for Financial Regulations in India

India’s regulators continue to refine the rules around emerging technology. Central Bank Digital Currency, or CBDC, pilots are already underway. The digital rupee could reshape how payments work across the country in the coming years.

Artificial intelligence in lending and credit scoring is also drawing regulatory attention. The RBI has signaled interest in setting clear guidelines for AI-driven financial decisions. This will likely shape how fintech companies build credit models going forward.

Open banking frameworks are expanding as well. Account aggregator systems now let users share financial data securely across institutions. This creates new opportunities for personalized financial products. However, it also raises fresh questions about consent and data security that regulators must address.

Fintech founders who track these changes closely will be better positioned to adapt. Building flexible systems that can adjust to new rules quickly will become a real competitive advantage. Staying engaged with industry bodies and regulatory updates is no longer optional for serious players.

Cybersecurity requirements are also likely to tighten. As digital transactions grow, regulators want stronger protection against fraud and cyberattacks. Fintech companies that invest early in robust security systems will avoid costly disruptions later.

How India’s Financial Regulations Are Shaping Fintech Innovation

Conclusion

India’s financial regulations continue to shape fintech innovation in powerful ways. Strong rules around KYC, data protection, and lending have built trust with millions of users. While compliance brings real challenges, it also creates a stronger, more sustainable market for everyone involved.

This balance between oversight and innovation is rare globally, and India has managed it better than most large economies. Founders who study this model closely can apply the same principles even beyond India’s borders.

Founders and business leaders who understand this regulatory landscape gain a real edge. They can build products that scale with confidence instead of facing surprises later. Treating compliance as a growth strategy, rather than a checkbox, sets strong fintech brands apart from the rest.

Build your authority with Digital Payment Guru, and position your fintech brand as a trusted name in this fast-moving industry. The founders who understand regulation today will shape the fintech products India relies on tomorrow.

Frequently Asked Questions About Financial Regulations

1. How do financial regulations in India affect fintech startups?

Financial regulations in India set clear rules for licensing, KYC, and data protection. These rules help fintech startups build trust and scale responsibly.

2. What role does the RBI play in fintech innovation?

The RBI creates guidelines for payments, lending, and data storage. This regulatory framework supports fintech innovation while protecting consumers from fraud and hidden fees.

3. Why is data localization important for fintech companies in India?

Data localization rules require companies to store Indian payment data locally. This builds trust and strengthens the country’s digital infrastructure over time.

4. What is a regulatory sandbox in fintech?

A regulatory sandbox lets startups test new financial products under RBI supervision. This helps companies innovate safely before facing full compliance requirements.

5. How will future regulations shape India’s fintech industry?

Future rules will likely address AI-driven lending, CBDC adoption, and open banking. Companies that adapt early will gain a strong competitive advantage.

Also Read:

Why Shoppers Abandon Mobile Carts, and How to Fix It

How to Handle Real-Time Payment Rules? Complete Guide

Â