How Should Businesses Reprice Their Products After UPI MDR Changes?...
Read More
How Should Businesses Reprice Their Products After UPI MDR Changes?...
Read More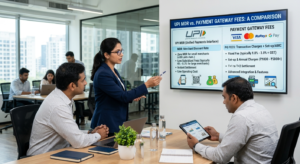
UPI MDR vs Payment Gateway Charges: What Will Actually Cost...
Read More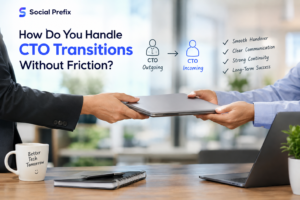
When Your Co-Founder CTO Steps Down: Maintaining Product Momentum During...
Read More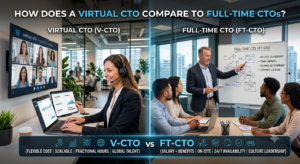
Virtual CTO for FinTech Startups: Architecting Banking API Integrations With...
Read More
VC Due Diligence Prep: 7 Architecture and Codebase Red Flags That Freeze Series A/B Funding (And How to Fix Them) VC due diligence can make or break a funding round. Founders often spend months perfecting their pitch deck. However, many overlook the technical review that follows. This is where deals frequently stall or collapse entirely. Picture a founder who has just wrapped up a strong pitch meeting. The investor seems interested and asks to move forward with due diligence. Weeks later, the deal quietly stalls. Often, the real reason is not the business model or the market opportunity. Instead, it is something buried in the codebase that nobody flagged early enough. Investors want confidence that your product can scale. They want proof that your team can move fast without breaking things. If your architecture or codebase raises concerns, VC due diligence can freeze your Series A or Series B round. This guide walks through seven common red flags. It also explains how founders can fix them before investors ever ask. Each red flag below reflects a pattern seen repeatedly across failed and delayed funding rounds. None of them are unusual or unique to a single industry. Instead, they represent common growing pains that many startups face as they scale from a small team to a larger, more complex organization. Why VC Due Diligence Goes Deeper Than the Pitch Many founders assume due diligence mainly covers financials and market size. In reality, technical due diligence has become just as important. Investors increasingly bring in engineering experts to review your codebase. They examine scalability, security, and long-term maintainability. Some funds now employ dedicated technical partners solely for this purpose, reflecting how much weight engineering quality carries in modern funding decisions. This shift makes sense. A great product idea means little if the underlying system cannot support growth. Consequently, founders who prepare early gain a real advantage. Understanding common red flags helps you address issues before they threaten your funding timeline. Technical due diligence typically involves a mix of interviews, automated code analysis, and hands-on review by experienced engineers. Investors want to understand not just what your product does today, but whether it can support the growth projections in your pitch deck. A mismatch between your technical reality and your growth story can quickly raise doubts, even if every other part of your business looks strong. Red Flag 1: Poor Code Documentation of VC Investors expect to see clear documentation. Without it, technical reviewers struggle to understand how your system works. This slows down the entire due diligence process and raises immediate concerns. The fix: Document your architecture, key workflows, and API structures. Keep documentation updated as your product evolves. Clear documentation signals a mature, well-managed engineering team. Consider assigning ownership of documentation to specific team members, so it does not fall through the cracks as your roadmap shifts. Red Flag 2: High Technical Debt Technical debt accumulates when teams prioritize speed over code quality. While some debt is normal, excessive debt raises red flags. It suggests future scalability problems and higher maintenance costs. The fix: Conduct regular code reviews and refactoring sprints. Track technical debt using a simple internal system. Show investors that you actively manage and reduce debt over time. Many founders find it helpful to dedicate a fixed percentage of each sprint specifically to debt reduction, rather than treating it as an afterthought. Red Flag 3: Lack of Automated Testing Manual testing alone cannot keep up with a growing codebase. Investors often ask about test coverage during VC due diligence. Low or missing automated tests suggest higher risk of bugs and downtime. The fix: Implement unit, integration, and end-to-end tests. Aim for solid coverage across critical features. Automated testing also speeds up future development, which investors appreciate. It also reduces the chance of production incidents during a high-visibility growth period, when your reputation with customers and investors matters most. Red Flag 4: Weak Security Practices Security gaps are a serious concern for any investor. This includes poor access controls, unencrypted data, or outdated dependencies. A single vulnerability can damage trust and delay funding significantly. The fix: Perform regular security audits. Update dependencies consistently. Implement strong authentication and data encryption practices. Document your security protocols clearly for investor review. If your product handles sensitive customer data, consider pursuing relevant compliance certifications early, since investors in regulated industries often ask about them directly. Red Flag 5: Single Points of Failure If your system relies heavily on one server, one engineer, or one vendor, this creates risk. Investors want to see resilience built into your architecture. Single points of failure suggest fragile infrastructure. The fix: Build redundancy into critical systems. Avoid over-reliance on any single team member for core knowledge. Cross-train your engineering team and document key processes thoroughly. Investors often ask what would happen if a key engineer left tomorrow, so having a clear answer builds confidence. Red Flag 6: Scalability Concerns Some codebases work fine at small scale but struggle under growth. Investors want evidence that your architecture can handle rapid user growth. Poor database design or inefficient code often signals future scaling problems. The fix: Stress test your systems before scaling rapidly. Optimize database queries and consider scalable infrastructure solutions early. Show a clear plan for handling increased demand. Presenting load testing results during due diligence can turn this red flag into a genuine strength. Red Flag 7: Messy or Inconsistent Codebase Structure A disorganized codebase slows down new developers and increases error rates. Investors view this as a sign of weak engineering discipline. It can also indicate rushed development without proper planning. The fix: Establish clear coding standards across your team. Use consistent naming conventions and folder structures. Regularly review code quality to maintain consistency as your team grows. Automated linting tools can help enforce these standards without adding extra manual review burden on your senior engineers. How to Prepare for VC Due Diligence Successfully Preparation is the key to passing technical due diligence smoothly. Start by conducting
Compliance Automation: Using AI to Stay Ahead of Regulations Regulations change constantly. New rules appear across finance, data privacy, and payments every year. Keeping up manually drains time and increases risk. This is where compliance automation becomes valuable. AI now helps businesses track, interpret, and apply regulatory changes faster than ever before. This guide explains how AI-powered compliance automation works. It also shows practical steps for adopting it, even without a large legal or compliance team. Whether you run a fintech startup or a growing enterprise, these strategies apply directly to your business. Why Traditional Compliance Methods Fall Short Traditional compliance relies heavily on manual review. Teams read updates, interpret language, and adjust policies by hand. This process is slow. It is also prone to human error. Furthermore, regulatory bodies release updates frequently and without much warning. A single missed update can lead to costly penalties. Small teams often struggle to monitor every relevant regulation across multiple regions. As businesses expand into new markets, compliance complexity multiplies. Different countries enforce different rules. Consequently, manual tracking becomes nearly impossible at scale. This is exactly where compliance automation proves its value. The Real Cost of Non-Compliance Non-compliance costs more than fines. It damages trust, delays product launches, and increases legal exposure. Additionally, repeated violations can trigger stricter regulatory scrutiny going forward. Many businesses underestimate these hidden costs. They focus only on avoiding direct penalties. However, reputational damage often outlasts any single fine. Proactive compliance protects both finances and brand reputation. Customers and partners also notice compliance failures. A public violation can slow down partnership deals or investor conversations for months. Building a reliable compliance record, therefore, supports growth well beyond the regulatory department. How AI Powers Compliance Automation AI-driven compliance tools scan regulatory updates continuously. They flag changes relevant to your industry. Moreover, they can map new rules directly against your existing policies. This process, once handled by large legal teams, now runs in the background. Machine learning models learn to recognize patterns across regulatory language. As a result, they can highlight risks faster than manual review ever could. Real-Time Regulatory Monitoring Real-time monitoring tools track changes from government agencies, financial regulators, and industry bodies. When something shifts, the system alerts your compliance team immediately. This speed matters. Early awareness allows businesses to adjust policies before violations occur. In contrast, delayed awareness often leads to reactive scrambling and last-minute fixes. Many platforms also let teams customize alert priority. High-risk regulatory changes trigger immediate notifications, while minor updates get grouped into weekly summaries. This filtering keeps teams focused on what truly matters. Automated Policy Mapping Beyond monitoring, AI tools can map regulations to internal policies automatically. They identify gaps between current practices and new requirements. Consequently, compliance teams spend less time searching and more time acting. This mapping process also creates useful documentation. Auditors appreciate clear records showing how policies evolved alongside regulatory changes. Why Manual Tracking No Longer Scales Manual tracking worked when regulations changed slowly. That era has ended. Regulators now update rules more frequently, and enforcement has grown stricter across most industries. A single compliance officer cannot realistically read every bulletin, guidance note, and amendment. Furthermore, cross-border businesses face multiplied complexity, since each region publishes its own updates on its own schedule. Automation closes this gap by working continuously in the background. Building a Compliance Automation Strategy Adopting compliance automation does not require a complete system overhaul. A phased approach works best for most businesses. Step 1: Audit Your Current Compliance Process Start by reviewing how compliance currently works. Identify manual bottlenecks. Note where delays or errors happen most often. This audit reveals where automation adds the most value. Step 2: Choose the Right AI Compliance Tools Not every tool fits every business. Look for platforms built for your specific industry, whether that is payments, healthcare, or general data privacy. Additionally, check integration options with your existing systems. Trial periods help here. Test how well a tool handles real regulatory scenarios before committing long term. This hands-on testing prevents costly mismatches later. Step 3: Train Staff on New Workflows Automation works best alongside informed staff. Teams still need to understand alerts and act on them appropriately. Therefore, short training sessions should accompany any new tool rollout. Encourage compliance staff to treat AI as a support system, not a replacement. Human judgment remains essential for complex regulatory decisions. Step 4: Monitor and Refine Continuously No automation system works perfectly from day one. Review alerts regularly. Adjust filters to reduce noise and improve accuracy. Over time, the system becomes more precise and more useful. Building Better Audit Trails Automated systems naturally create detailed logs of every action taken. This includes which regulation triggered an alert and how the team responded. Auditors value this level of detail highly. Additionally, clear audit trails reduce the time needed for external reviews. Instead of reconstructing history manually, compliance teams simply export existing records. This efficiency saves both time and legal expense during audits. Compliance Automation in the Payments Industry Payment companies face some of the strictest regulatory environments. Rules around fraud prevention, data security, and cross-border transactions shift often. AI-powered compliance tools help payment businesses stay ahead of these changes. For example, automated systems can flag suspicious transaction patterns instantly. They can also update fraud detection rules as new regulations emerge. Similarly, they help maintain accurate audit trails required by financial regulators. This proactive approach reduces both regulatory risk and operational strain. Teams no longer chase every update manually. Instead, they focus on strategic decisions while automation handles routine monitoring. Reducing Risk Without Increasing Headcount Many payment businesses cannot afford large compliance teams. AI-powered automation closes this gap effectively. It allows small teams to manage complex regulatory environments confidently. Finally, this efficiency creates room for growth. Businesses can expand into new markets without proportionally expanding their compliance staff. Common Challenges in Compliance Automation Adoption is not always smooth. Some businesses face resistance from staff accustomed to manual processes. Others struggle with poor data quality, which
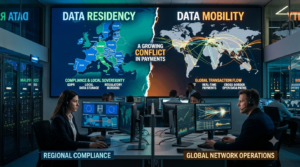
Data Residency vs Data Mobility: A Growing Conflict in Payments Introduction Payment companies move money across borders every second. However, data does not always move as freely as the transactions it supports. This is where data residency vs data mobility becomes a real challenge. Data residency laws require certain information to stay within a country’s borders. Data mobility, on the other hand, pushes for fast, flexible movement of data across systems and regions. These two forces often pull payment companies in opposite directions. This article explains what each concept means, why the conflict is growing, and how payment businesses can manage both without slowing down growth. Whether you lead compliance, technology, or product strategy, understanding this balance is essential. By the end of this guide, you will have a clearer picture of the trade-offs involved. You will also walk away with practical steps for aligning compliance goals with operational speed. What Data Residency Really Means for Payments Data residency refers to laws that require data to be stored within a specific country or region. Many governments created these rules to protect citizen privacy and financial stability. For payment companies, this often means customer transaction data must stay on local servers. Countries like India, Russia, and several EU nations enforce strict residency requirements. Non-compliance can lead to heavy fines or loss of operating licenses. These rules exist for good reasons. Governments want control over sensitive financial data. They also want faster access during audits or investigations. As a result, residency requirements continue to expand across new markets. However, strict residency rules create real operational challenges. Payment companies must build separate data infrastructure in each region. This increases both cost and complexity significantly. Enforcement is also becoming stricter. Regulators now conduct more frequent audits and demand faster proof of compliance. Companies that once treated residency as a checkbox item now face real operational scrutiny. Smaller fintech firms often feel this pressure most. Limited budgets make it harder to stand up local infrastructure in every market. As a result, expansion plans sometimes stall over residency requirements alone. Cloud providers have responded by expanding regional data centers. Major platforms now offer local storage options in dozens of countries. This makes compliance easier, though costs still rise with each new region added. Contracts with local banking partners often add another residency layer. Many agreements require certain transaction records to remain in-country for a set retention period, adding further storage obligations beyond the core payment data itself. Even record deletion falls under these rules in many regions. Some laws dictate not just where data lives, but how long it must be kept and when it must be permanently erased. Some jurisdictions also require a local data protection officer. This adds a staffing requirement on top of the technical infrastructure needed to satisfy residency laws. Why Data Mobility Matters for Global Payment Systems Data mobility allows information to move freely between systems, clouds, and countries. This flexibility supports faster fraud detection, better analytics, and smoother customer experiences. Global payment providers rely on mobility to process transactions in real time. For example, a purchase made in Singapore might require instant verification through a system hosted elsewhere. Mobility makes this possible. Without data mobility, companies struggle to build unified fraud models. Local-only data limits visibility into cross-border patterns. Consequently, fraud detection becomes slower and less accurate. Mobility also supports innovation. Centralized data lets teams build better machine learning models. These models improve risk scoring, personalization, and customer support across every market a company serves. Operational efficiency improves too. When teams access a single, unified dataset, they avoid duplicate systems and conflicting reports. This saves both time and engineering resources across the organization. Customer experience benefits directly from mobility as well. Shoppers expect fast checkouts regardless of where they are located. Restricting data flow can introduce delays that frustrate users and increase cart abandonment. Mobility also enables better disaster recovery. When data can move between regions, companies can shift processing during outages without interrupting service. This resilience becomes critical during peak shopping periods or system failures. Partnership opportunities expand with mobility too. Payment companies often integrate with global partners for fraud scoring or currency conversion. These integrations depend on data flowing smoothly between systems in different countries. Where Data Residency vs Data Mobility Creates Conflict The tension between these two priorities shows up clearly in cross-border payments. A transaction may involve banks in three different countries, each with its own residency rules. Meanwhile, fraud detection systems need access to global data patterns to work effectively. Restricting data to one country limits how well these systems can identify emerging threats. This conflict also affects vendor selection. Cloud providers must offer local data centers in every region where a company operates. This adds cost and complicates system architecture. Regulatory differences make things harder still. Rules in one country may directly contradict expectations in another. Payment companies must navigate this patchwork carefully to avoid compliance failures. Technology architecture often becomes a bottleneck too. Legacy systems built for a single region rarely support distributed storage well. Rebuilding this infrastructure takes time, money, and careful coordination across teams. Legal teams and engineering teams sometimes work in isolation, which makes this conflict worse. Without close collaboration, technical solutions may satisfy engineers but still fail to meet legal requirements. Merger and acquisition activity adds even more complexity. Combining payment platforms across borders often means reconciling two different residency approaches at once, which can delay integration timelines significantly. Customer trust sits at the center of this conflict too. Users want fast service, but they also want assurance that their financial data stays protected under local law. Balancing both expectations requires careful communication. How Payment Companies Can Balance Both Priorities Smart payment companies use hybrid data architecture to manage this conflict. Sensitive personal data stays local, while anonymized or aggregated data moves freely for analytics. Data localization tools also help. These systems automatically route data storage based on regional requirements. This reduces manual work and lowers compliance risk

How India’s Financial Regulations Are Shaping Fintech Innovation Introduction India’s fintech sector is growing at a remarkable pace. Millions of people now use digital payments, lending apps, and online banking every day. Behind this growth sits a strong framework of financial regulations in India. These rules shape how fintech companies build products and reach customers. This article explores how India’s financial regulations are shaping fintech innovation. You will learn which rules matter most, how they affect startups, and what founders should expect next. Business owners, technical managers, and digital marketers will find practical insight here. Additionally, this guide explains complex rules in simple terms. India now has one of the largest digital payment markets in the world. This scale did not happen without careful oversight. Regulators and innovators have worked together, sometimes with friction, to build a system that millions trust every day. The Regulatory Foundation Behind India’s Fintech Boom India’s fintech growth did not happen by accident. The Reserve Bank of India, or RBI, built a strong foundation for digital finance. This foundation includes the Unified Payments Interface, known as UPI, which now processes billions of transactions each month. The RBI also created clear licensing rules for payment banks and non-banking financial companies. These rules give fintech startups a path to operate legally. As a result, entrepreneurs know what steps to follow before launching a product. This clarity reduces risk for investors too. Data protection has become a growing focus for regulators. The Digital Personal Data Protection Act sets rules for how companies collect and store user data. Fintech companies must follow these rules carefully. Consequently, product teams now build privacy into their apps from day one, not as an afterthought. Regulatory sandboxes have also played a key role. The RBI allows selected startups to test new products in a controlled environment. This helps regulators understand new technology before writing formal rules. Meanwhile, startups get real feedback without facing the full weight of compliance too early. The Securities and Exchange Board of India, or SEBI, also shapes fintech through rules for investment platforms and wealth-tech apps. Together, these bodies form a layered system of oversight. Each layer targets a different part of the financial ecosystem, from payments to lending to investing. The Insurance Regulatory and Development Authority of India, known as IRDAI, plays a similar role for insurtech startups. This layered approach means fintech founders must understand more than one regulator, depending on which financial services they offer. How Compliance Rules Push Financial Regulation Forward Many founders assume regulation slows down innovation. In India’s fintech space, the opposite has often proven true. Clear rules create trust, and trust drives adoption among cautious users. Know Your Customer, or KYC, requirements are a good example. These rules force fintech apps to verify user identity before opening an account. This process once took days using paper documents. Today, video KYC and Hadar-based verification make on-boarding fast and secure. Therefore, compliance rules pushed companies to build better technology. Similarly, RBI guidelines on data localization require companies to store Indian payment data within the country. This rule pushed fintech firms to invest in local cloud infrastructure. In turn, this investment supported the growth of India’s broader technology ecosystem. Payment aggregator and payment gateway rules also raised the bar for security. Companies must now meet strict standards before processing transactions. This has reduced fraud and increased consumer confidence in digital payments. In contrast, markets with weaker rules often see slower adoption due to trust issues. Lending regulations have reshaped how digital lenders operate too. The RBI’s digital lending guidelines require clear disclosure of interest rates and fees. This protects consumers from hidden charges. Fintech lenders that comply well often see stronger customer loyalty as a direct result. Similarly, rules around recovery practices have pushed lenders to build more respectful collection processes. Aggressive tactics that once damaged brand reputation are now restricted by law. This shift has encouraged fintech lenders to invest in better customer support systems instead. Challenges Fintech Startups Face Under Current Financial Regulations Regulation is not without its challenges for fintech startups. Compliance costs can be high, especially for early-stage companies. Building systems for KYC, data protection, and reporting requires time and money that small teams may not have. Frequent regulatory updates also create uncertainty. The RBI and other bodies update guidelines regularly to keep pace with new technology. Startups must stay alert and adjust their products quickly. Otherwise, they risk falling out of compliance without realizing it. Cross-border payment rules add another layer of complexity. Fintech companies working with international partners must navigate both Indian rules and foreign regulations. This dual compliance burden can slow product launches significantly. Despite these challenges, most founders agree that strong regulation ultimately builds a healthier market. It filters out weak players and rewards companies that invest in proper systems. Thus, long-term winners in India’s fintech space tend to be those who treat compliance as a strategic advantage, not a burden. Smaller startups often partner with compliance experts to manage this load. This allows founders to focus on product and growth while specialists handle regulatory details. This approach has become common across the industry. Talent shortages also add pressure. Skilled compliance officers who understand both finance and technology are hard to find. Fintech companies often compete with banks and larger financial institutions for the same limited pool of experts. This drives up hiring costs for early-stage teams. Investor expectations have shifted as a result of these challenges. Venture capital firms now look closely at a startup’s compliance readiness before writing a check. A strong regulatory foundation has become just as important as a strong product in fundraising conversations. What’s Next for Financial Regulations in India India’s regulators continue to refine the rules around emerging technology. Central Bank Digital Currency, or CBDC, pilots are already underway. The digital rupee could reshape how payments work across the country in the coming years. Artificial intelligence in lending and credit scoring is also drawing regulatory attention. The RBI has signaled

The Rise of Real-Time Payment Regulations Across the World Money now moves faster than ever. A payment that once took days can settle in seconds. This speed has changed how people shop, pay bills, and run businesses. Governments have taken notice. As instant payments grow, so does the need for rules to protect them. This has led to a wave of real-time payment regulations across the world. This blog explains why these regulations exist. It also covers how they affect banks, businesses, and consumers. By the end, you will understand this fast-moving area of financial law. Financial leaders cannot afford to ignore these changes. Whether you run a bank, a fin-tech startup, or a business that accepts payments, new rules will likely touch your operations soon. Why Real-Time Payments Needed New Rules Traditional payment systems had built-in delays. These delays gave banks time to catch fraud or reverse mistakes. Real-time payments remove that safety net. Once money moves, it usually cannot be recalled. This creates new risks for fraud and error. Regulators stepped in to close these gaps and protect users. Additionally, real-time systems connect many players. Banks, fin-tech firms, and payment networks all work together. Without shared rules, this connection could create weak points. Clear regulations help keep the whole system secure. Cybercriminals also adapt quickly to new technology. Instant payments give them a narrow window to strike before anyone notices. Regulators respond by requiring stronger identity checks and real-time fraud monitoring across payment networks. Consumer trust also plays a role. People need confidence that instant payments are safe. Strong rules build that confidence and encourage wider adoption of digital payment tools. Small businesses depend on this trust too. Many now rely on instant payments for daily cash flow. A single fraud incident without clear recourse could damage their operations severely. Regulation gives these businesses a safety net they can count on. Regulators also aim to prevent systemic risk. If one part of a connected payment network fails, the effects could spread quickly. Clear rules help contain problems before they threaten the wider financial system. Key Real-Time Payment Regulations Around the World Different regions have taken different approaches. The European Union created the Instant Payments Regulation. This law requires banks to offer instant transfers at the same cost as regular transfers. In the United States, the Federal Reserve launched FedNow. This system supports instant payments across banks. Regulators continue to build rules around fraud prevention and dispute handling for this network. India has developed strong oversight for its Unified Payments Interface, known as UPI. The Reserve Bank of India monitors transaction limits, fraud controls, and data protection closely. Meanwhile, countries like Brazil and Australia have introduced similar frameworks. Brazil’s Pix system and Australia’s New Payments Platform both operate under strict regulatory guidelines. These rules cover security, availability, and consumer protection. As a result, a global pattern is forming. Regulators everywhere are focusing on similar goals: speed, safety, and fairness for users. Africa is also emerging as a leader in this space. Kenya’s mobile money systems, closely watched by regulators, paved the way for instant payments long before many wealthier nations. Other African nations now study this model closely. China offers another example worth noting. Its digital payment giants operate under strict government oversight. Regulators there focus heavily on data privacy and anti-money laundering controls within instant payment networks. The United Kingdom continues refining its Faster Payments system as well. Regulators there recently introduced stricter rules around reimbursing victims of payment fraud, placing more responsibility on banks to protect customers. Southeast Asian nations, including Singapore and Thailand, have linked their real-time payment systems together. This cross-border integration required careful regulatory coordination between multiple central banks and financial authorities. How These Regulations Affect Businesses Businesses that accept payments must follow these new rules closely. Non-compliance can lead to fines or loss of payment access. This makes regulatory awareness essential for finance teams. Companies must also update their fraud detection systems. Real-time payments leave little room for manual review. Automated tools now need to catch suspicious activity within seconds, not hours. Furthermore, businesses operating across borders face extra complexity. Each country may have different rules for instant payments. A company selling in multiple regions must track and follow each set of requirements. On the positive side, compliance often improves trust with customers and partners. Businesses that follow real-time payment regulations well can process payments faster and more reliably. This can become a real competitive advantage. Reporting requirements add another layer of responsibility. Many regulations require businesses to log transaction data and report suspicious activity within tight deadlines. Building systems that support this reporting takes time and investment. Vendor selection also shifts under these rules. Businesses often choose payment processors based on their compliance track record. A provider with strong regulatory alignment can reduce a company’s own compliance burden significantly. Challenges in Enforcing Real-Time Payment Regulations Enforcement is not always simple. Real-time payments cross borders instantly, but laws are often written for single countries. This mismatch creates gaps that bad actors can exploit. Regulators also struggle to keep pace with new technology. Payment methods evolve quickly, and rules can lag behind. This forces frequent updates to existing regulations. Another challenge involves smaller financial institutions. Large banks often have resources to meet complex rules quickly. Smaller banks or fin-tech startups may find compliance costly and difficult to manage. Despite these hurdles, cooperation between countries is improving. International bodies now share information and best practices. This collaboration helps close gaps and strengthen global payment security. Legacy systems present a further obstacle. Some banks still run on decades-old infrastructure. Upgrading these systems to meet real-time regulatory standards can take years and significant financial investment. Consumer education remains an ongoing challenge as well. Many users do not fully understand how instant payments work or what protections apply. Regulators and businesses must work together to close this knowledge gap. Staffing shortages within regulatory bodies add further strain. Reviewing complex payment systems requires specialized expertise, and many agencies

How vCTO Services Help You Avoid Shiny-Object Syndrome in Tech Adoption New technology launches almost every week. It is tempting to chase every trending tool. However, this habit often leads to wasted time, scattered focus, and money spent on the wrong priorities. This pattern is known as shiny-object syndrome. Teams jump from tool to tool without a clear strategy. As a result, technology decisions become reactive instead of thoughtful, and budgets quietly drift away from what the business actually needs. vCTO services offer a practical solution to this problem. A virtual chief technology officer brings structure and experience. In this blog, we will explore how vCTO services help businesses adopt technology wisely, from evaluating new tools to building a sustainable long-term road map. What Is Shiny-Object Syndrome in Tech Adoption? Shiny-object syndrome happens when teams chase new tools constantly. They adopt trending software without checking if it solves a real problem. This often leads to fragmented systems and wasted budgets. Many startups fall into this trap early. Excitement around new AI tools or platforms can override careful planning. Consequently, teams end up with too many overlapping tools that quietly compete for the same job. This problem also affects larger companies. Departments adopt tools independently, without company-wide coordination. Over time, this creates messy tech stacks that are hard to manage. The root cause is usually a lack of clear technology strategy. Without a plan, every new trend looks appealing. This is exactly where vCTO services can make a difference. Why Shiny-Object Syndrome Feels So Tempting New tools often promise instant results with minimal effort. Marketing around trendy software tends to highlight quick wins. Naturally, busy teams find these promises hard to resist. Social proof adds pressure, too. When competitors mention a new tool publicly, teams worry about falling behind. This fear-driven decision-making rarely leads to sound technology choices. Understanding these psychological triggers helps teams pause before acting. Recognizing the pattern is the first step toward avoiding it. This is precisely where structured guidance becomes valuable. What Do vCTO Services Actually Do? A vCTO, or virtual chief technology officer, provides strategic tech leadership. Unlike a full-time hire, this role is flexible and often part-time. Businesses get expert guidance without the cost of a permanent executive. vCTO services typically include technology road mapping and vendor evaluation. They also cover architecture decisions and team guidance. This support helps businesses avoid random, uncoordinated tech choices. Additionally, a vCTO evaluates tools against real business goals. Instead of asking “is this trendy,” they ask “does this solve our problem.” This shift in thinking prevents impulsive technology purchases. Many startups use vCTO services during early growth stages. At this point, technical decisions have long-term consequences. A wrong choice can be expensive to reverse later, especially once a whole team has built workflows around it. Established businesses also benefit from vCTO services during digital transformation. Modernizing legacy systems requires careful planning. A vCTO ensures new technology fits existing infrastructure smoothly. The Difference Between A vCTO And A Consultant A general consultant often provides one-time advice on a specific project. A vCTO, however, stays involved over time as an ongoing strategic partner. This continuity allows for more consistent, informed decision-making. Consultants may not fully understand a company’s internal culture or constraints. A vCTO builds that understanding gradually through regular involvement. As a result, their recommendations tend to fit the business more naturally. This ongoing relationship also means faster response times. When a new tool trend emerges, a vCTO can quickly assess it. Businesses avoid delays that come from starting evaluations from scratch each time. How vCTO Services Prevent Shiny-Object Syndrome First, vCTO services introduce a structured evaluation process. Every new tool gets reviewed against clear criteria. This prevents teams from adopting software based on hype alone. Second, a vCTO focuses on long-term technology strategy. Instead of quick fixes, they build road maps aligned with business goals. This approach naturally filters out unnecessary trendy tools that promise short-term excitement but little lasting value. Third, vCTO services bring outside experience to internal decisions. Many tech trends look impressive but fail in practice. An experienced vCTO has often seen these patterns before, having watched similar tools rise and fade across other client engagements. Moreover, a vCTO helps teams measure return on investment. Before adopting new technology, they calculate expected value. This data-driven approach reduces emotional or impulsive tech decisions across every department, not just engineering. vCTO services also improve internal communication around tech choices. Teams understand why certain tools are approved or rejected. As a result, shiny-object requests decrease significantly over time. Finally, a vCTO builds a repeatable decision framework. Future technology choices become faster and more consistent. This framework protects the business long after initial adoption decisions are made. A Simple Framework vCTOs Often Use Most vCTOs start by asking what specific problem a tool solves. If the answer is vague, the tool likely does not deserve further evaluation. This single question filters out a large share of shiny-object requests early. Next, they assess integration effort against existing systems. A tool that looks impressive alone may create friction elsewhere. Weighing this trade-off prevents costly compatibility issues down the road. Finally, they estimate the total cost of ownership, not just the sticker price. Training time, maintenance, and support all factor into this calculation. This complete picture leads to far more responsible technology adoption decisions. Signs Your Business Needs vCTO Services If your company constantly switches tools, this is a warning sign. Frequent tool changes usually signal a lack of clear strategy. vCTO services can help stabilize this pattern quickly. Another sign is overlapping software subscriptions. If multiple teams use similar tools separately, costs add up fast. A vCTO can consolidate these choices efficiently. Businesses without technical leadership often struggle here, too. Non-technical founders may feel unsure evaluating complex tech options. vCTO services fill this expertise gap affordably, without the overhead of a full executive hire. Additionally, if technology decisions feel reactive rather than planned, it is time for guidance. A vCTO shifts